Global Settings
Control the general behavior of the Reemo platform: security, user accounts, remote sessions and instance branding.
Access: verified_user Admin Area > build System > settings Global Settings.
User creation
Define the rules for creating and securing user accounts.
Set the password rules
Minimum password length: minimum number of characters (default 8). Recommendation: at least 12 characters for sensitive environments.
Password requires letters: requires at least 1 lowercase letter (a-z) and 1 uppercase letter (A-Z).
Password requires digits: requires at least 1 digit (0-9).
Password requires special characters: requires at least 1 special character.
These rules reduce the risk of brute-force or dictionary attacks.
Allow organization admins to manage users
Choose what organization administrators can do without going through you.
Allow organization admin to edit managed users password: lets organization administrators change the password of managed users (creation and editing). Useful for organizations without centralized SSO.
Allow organization admin to invite external users: lets organization administrators invite users from other organizations by email.
Limit sign-ups by email domain
Restrict which email addresses can sign up. Separate domains with a comma (example: domain.com, *.domain.com).
Whitelisted domains: only users whose email address matches these domains can sign up. Use it to prevent unwanted external signups.
Enable domain blacklist: turns on domain exclusion at sign-up.
Blacklisted domains: domains excluded from sign-up (for example
gmail.com), to limit risks from personal emails.
Note
A strong password policy combined with multi-factor authentication (2FA) is essential to ensure instance security.
Signin
Control how users sign in to the portal: authentication, account lockout and session duration.
Enforce 2FA, restrict built-in authentication and filter IPs
Strengthen how users prove their identity.
Force Two-Factor Authentication for sign-in: requires all users to enable two-factor authentication (2FA). Strongly recommended.
Enable Internal 2FA for users without 2FA enabled: users without 2FA must go through an internal verification (email) before accessing the portal.
Disable Built-In Authentication for SAML/LDAP Users: forces these users to sign in exclusively through SSO.
Built-in authentication IP filter: restricts access to specific IP ranges, for example the internal network only. Examples:
192.168.0.*or10.0.0.1.
Alert on unknown devices and lock accounts after failures
Spot suspicious sign-ins and temporarily block accounts targeted by repeated attempts.
Send unknown devices emails on sign-in: sends an email each time a user signs in from a new device. Recommended for detecting suspicious sign-ins.
Failed attempts before lockout and Lockout duration: after this many wrong passwords in a row, the account is locked and the user must wait for the lockout duration, in minutes, before signing in again. A successful sign-in resets the counter. An administrator cannot unlock an account before the duration ends.
Defaults: 4 attempts and 10 minutes. Applies to built-in (Reemo password) and LDAP sign-ins.
Set up sessions and the logout shortcut
Decide how long and on how many devices a session stays open.
Disable “Remember Me”: removes the persistent session cookie. Enable this for critical environments.
Allow multiple HTTP sessions: allows a user to be signed in on multiple devices at the same time. Useful for mobile users, but reduces security.
Note
While this option is disabled, the Active Devices section in the user settings lists no sessions.
Auto Disconnect on Idle Portal Sessions (value in minutes): ends the session after the chosen period of inactivity (30 minutes by default). Recommendation: 15 to 20 minutes for sensitive environments.
Portal Logout Keyboard Shortcut: allows the instance administrator to define a key combination. Any user of the instance can use it to sign out of the portal, even in the middle of a session on a machine. Disabled by default.
To record it, enable the modifiers you want (Ctrl, Alt/Opt, Shift, Win/Cmd), click the key button, then press the key to record. A combination pressed at once is recorded immediately, and Esc cancels.
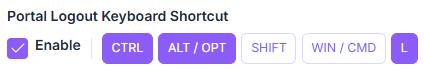
Ctrl + Alt + L shortcut recorded.
The physical key is saved, so the shortcut works on any keyboard layout, and each user sees it labelled for their own keyboard.
Note
Once configured, the shortcut applies to the whole instance, and users cannot disable it individually. It also appears, read-only, in each user’s Keyboard Shortcuts panel.
Remote Sessions
Control the behavior of remote sessions and how the instance displays machines.
Remote Session Restrictions
Admin can connect to any computer: when enabled, an instance administrator can directly connect to all registered machines. Useful for global support, but should be restricted to reduce abuse risk.
Synchronize machine names with the agent hostname: when enabled, the machine name is updated automatically from the hostname reported by the Reemo agent. The displayed name thus stays consistent with the actual system state.
Warning
Once this synchronization is active, the machine name is locked: it can no longer be modified manually from the computer’s profile.
Session Policies
Define the permissions and restrictions applied globally to remote sessions.
Note
These settings apply to the instance. Specific organizations can override them later (see Session Policies).
Each setting has a two-state dropdown (Enabled / Disabled) and a Not Locked / Locked toggle.
Reemo settings cascade through five levels — each can inherit a setting from the level above, and lock it for the levels below.
Level |
Inherit from above |
Lock for levels below |
|---|---|---|
Instance |
— |
Yes |
Organization |
Yes |
Yes |
Group |
Yes |
Yes |
Computer |
Yes |
Yes |
Computer-User assignment |
Yes |
— |
Clipboard
Clipboard Read: controls whether users can read the clipboard of remote devices.
Clipboard Write: controls whether users can write to the clipboard of remote devices.
Sessions
Auto Disconnect on Idle Sessions: defines whether a session ends automatically after a period of inactivity.
Custom TURN
Configure your own TURN servers for Reemo network transport when direct (P2P) connections fail.
Enable custom TURN configuration: when checked, these TURN servers are used to connect to the instance’s computers. Useful for relays hosted internally, to improve latency or comply with regulations.
TURN 1 and TURN 2: one block of fields per server:
Host: IP address or FQDN of the server.
Port: port of the server.
Authentication: authentication mode. With Username and password, every client receives the same credentials, which never change.
Username and Password: credentials of the server.
Note
This configuration is used by default if no other TURN server is set at the organization level.
Tip
For distributed environments, configure multiple TURN servers geographically close to users.
Containers
Limit the lifetime of the instance’s containers and set user access to their workstation.
Containers Max Expiration (in minutes): defines the maximum lifetime of a container after launch. Once expired, it is automatically destroyed or restarted depending on the configuration.
The user can access the workstation during the creation of the container: when checked, the user can access their workstation as soon as the container is created.
Note
The expiration limit applies to the maximum value allowed in a container profile of an organization.
Features
Turn platform features on or off for the whole instance.
Cloud Providers Enabled: lets you use Cloud Providers to provision computers. See Configure Cloud Providers.
Secure Keys Enabled: lets users sign in to the instance with Secure Keys.
Websocket Relays Enabled: lets you use Websocket Relays to connect to containers. See Configure Relay Servers.
These options are available only for Private Cloud and On-Premises deployments:
Workspaces Enabled: enables Workspaces and Workspace Services.
Workstations Enabled: enables Workstations (VM on container).
File Co-editing: enables co-editing on files in the file server.
Alerting enabled: makes the Alerting console available to instance administrators and to the organizations you allow. See Alerting.
Email
Email Notifications
Choose the automatic notifications sent by the instance:
Send unknown devices emails on sign-in: users receive an email each time they sign in from a new device.
Send emails when joining an organization: users receive an email each time they join an organization.
Send emails on organizations managed users creation: managed users receive an email when their account is created in the organization.
Access Request Notifications
Configure how approvers are alerted when users submit access requests for the approval workflow. The in-app notification tray is always populated, regardless of these settings.
Email approvers when a request is submitted: notifies the resource’s assigned approvers by email so they can review the request.
Auto-open the approval dialog on new requests: opens the approval dialog as soon as a new request arrives, without clicking the tray. The tray badge appears either way.
Webhook URL (Slack-compatible): optionally posts a JSON payload with a link to the approval modal for each new request. Leave empty to disable.
Each organization can keep or disable emails, add its own webhook (Slack, Microsoft Teams or JSON) and enable a reminder for pending requests (see Approval Workflow).
See also
Access Requests — Follow the requests submitted across all organizations.
SSO
Allow organizations to configure their own SSO connectors:
LDAP: sign-in based on an internal directory.
SAML: integration with an identity provider (IdP).
Note
If you only have one SSO, it is recommended to configure an SSO connector at the instance level rather than at the organization level.
Customization
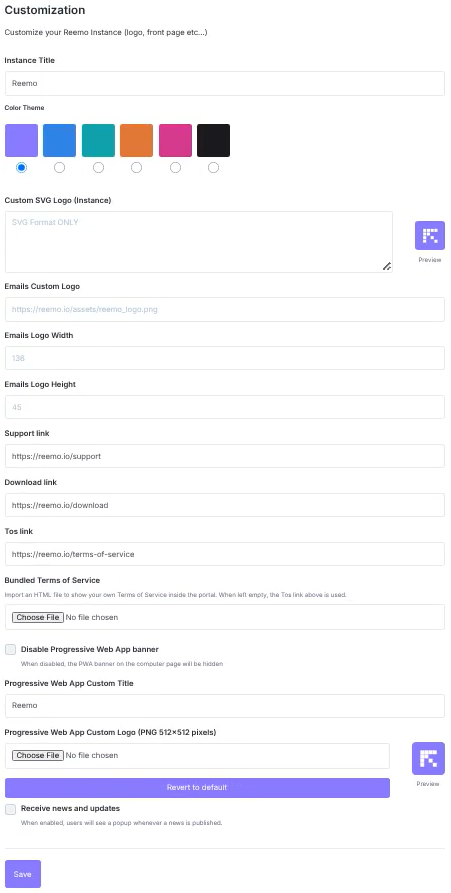
Instance customization
Adapt the appearance and branding of the instance:
Instance title: displayed on the portal.
Theme color: several predefined colors.
SVG logo: used in the interface and login screen.
Custom email logo: adjustable size (width and height).
Custom links: support, download, terms of use.
Bundled Terms of Service: import an HTML file to display custom Terms of Service inside the portal. When not set, the Tos link above is used.
Progressive Web App (PWA): customization of the title and icon (512x512) of the PWA added to the desktop.
Note
The Bundled Terms of Service option is available for Private Cloud and On-Premises deployments only.
Export instance
Export the complete instance configuration to a JSON file, to import it into another Reemo instance or use it as a backup.
Include private/secret keys: exports API keys, organizations, and groups.
Reset database on import: erases all existing data before import.
Warning
Remote Desktops are not exported, only containers.
Export may generate a high load on the database.
Handle this file with care: it contains sensitive information.
See also
Securing Your Instance — Overview of the controls that protect your instance.